
Blog Entries

16. 11. 2026 Leonardo Bambini Cloud, DevOps

From CAPEX to OPEX: How Cloud Computing Has Changed IT Costs

Introduction: A New Way to Build IT Infrastructure Cloud computing has fundamentally changed how businesses build, deploy, and pay for their products and services. Traditionally, companies had to purchase and maintain their own physical infrastructure, including servers, networking equipment, and storage systems. Today, they can rent computing resources from cloud providers and use someone else’s…

Read More
16. 11. 2026 Daniele Saccon APM, NetEye

How to Reveal Tornado’s Hidden Performance Issues

Tornado is a core NetEye component for event management. To ensure Tornado processes events and triggers the expected actions, you should monitor both service availability and its behavior under load. This article explains how to collect Tornado performance data with OpenTelemetry (OTel), send it to Elastic APM, and view it in Kibana in the NetEye…

Read More
13. 11. 2026 Marco Pergher CTF Writeups, Development, Events

WP CTF 2026 Bolzano: Cybersecurity “Capture the Flag”

WP CTF 2026: Five Editions. One Mission. Capture the Flag(s).  Würth IT Italy’s cybersecurity competition returns to Bolzano this November 28th, bringing together the next generation of cybersecurity talent.  Think fast. Dig deeper. Find the vulnerability. Capture the flag(s).  On Saturday, November 28, 2026, WP CTF returns to Bozen/Bolzano for its fifth edition. Organized by…

Read More
12. 11. 2026 Marco Pergher Atlassian, Events, Service Management

Atlassian Partner Solution Day in Milan, Where Monitoring Meets Service Management 

Atlassian Partner Solution Day 2026 in Milan: Monitoring and Service Management

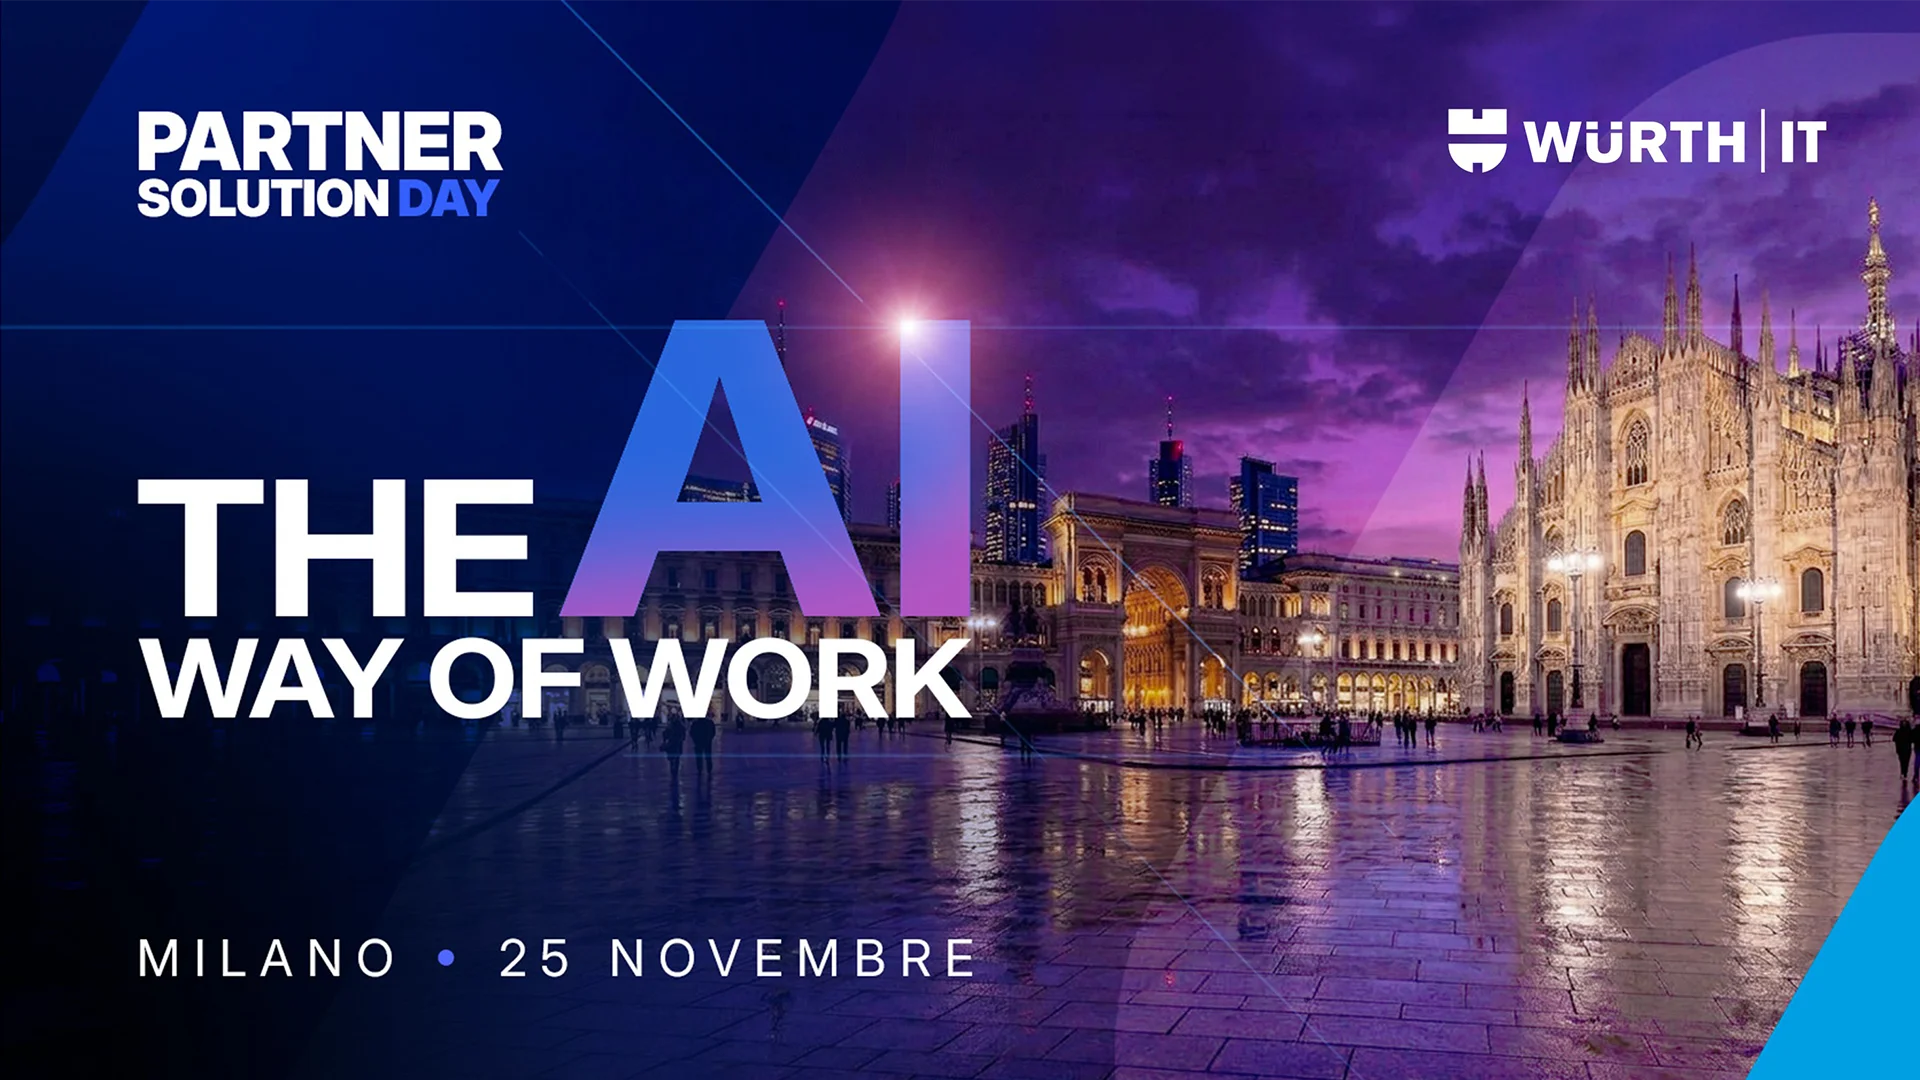
Join Us at the Atlassian Partner Solution Day in Milan, Where Monitoring Meets Service Management  On 25 November 2026, Würth IT Italy will take part in Atlassian Partner Solution Day at Gadames57 (Strada Privata Gadames 57) in Milan. Under the theme “The AI Way of Work,” the event brings customers and Atlassian together to explore…

Read More
11. 11. 2026 Patrick Harasser Bug Fixes, NetEye

Bug Fixes for NetEye 4.50

Social login provider icons are displayed correctly again We fixed an issue on the NetEye login page where icons of social login providers (identity providers configured in Keycloak) were rendered at the wrong size after the update to Keycloak 26.8. This made the login buttons look broken. The icons are now shown at a consistent…

Read More
11. 11. 2026 Patrick Harasser Bug Fixes, NetEye

NetEye 4 – Security Advisory (Grafana)

Disclaimer: The CVEs referenced below have not yet been publicly disclosed, so details regarding their severity, impact, and potential attack vectors are not available at this time. This post will be updated as soon as additional information becomes publicly available. Update: The CVEs referenced below have now been publicly disclosed, and additional details have been…

Read More
10. 11. 2026 Francesco Pavanello SEC4U, Threat Intelligence

Insider Threats Evolution in 2026

Executive Overview In 2026, the insider cyber threat landscape underwent a fundamental transformation driven by macroeconomic pressures, active monetization in the cyber-crime underground, and the widespread enterprise integration of autonomous artificial intelligence systems [1]. While negligent insiders misplacing devices or succumbing to phishing lures continue to account for a high volume of operational exposure, malicious…

Read More
10. 11. 2026 Damiano Chini Bug Fixes, NetEye

NetEye 4 – Security Advisory (ClickHouse)

Important: ClickHouse security update Type/Severity NetEye Product Security has rated this update as having a CRITICAL security impact. Topic An update for the clickhouse-server package is now available for NetEye 4. Security Fix for NetEye 4.50: Security Fixes This vulnerability is a remote code execution flaw in ClickHouse Server. It comes from an integer overflow (CWE-190). Under…

Read More
06. 11. 2026 Patrick Harasser Bug Fixes, NetEye

NetEye 4 – Security Advisory (Icinga Web 2)

Disclaimer: Three of the security issues referenced below do not yet have public CVE identifiers, so they are referenced by their GHSA ID. This post will be updated as soon as CVEs become available. Important: Icinga Web 2 security update Type/Severity NetEye Product Security has rated this update as having a High security impact. Topic…

Read More
06. 11. 2026 Patrick Harasser Bug Fixes, NetEye

NetEye 4 – Security Advisory (Keycloak)

Disclaimer: Some of the CVEs referenced below have not yet been publicly disclosed, so details regarding their severity, impact, and potential attack vectors are not fully available at this time. This post will be updated as soon as additional information becomes available. Important: Keycloak security update Type/Severity NetEye Product Security has rated this update as…

Read More
04. 11. 2026 Patrick Harasser Bug Fixes, NetEye

NetEye 4 – Security Advisory (Elastic Stack)

Important: Elastic Stack security update Type/Severity NetEye Product Security has rated this update as having a High security impact. Topic Updates for the Elastic Stack packages are now available for NetEye 4. Security Fix for NetEye 4.50 CVEs Elasticsearch Kibana Logstash Logstash shares the two eMudhra trust-store CVEs listed under Elasticsearch (CVE-2026-91403, CVE-2026-114820) through its…

Read More
03. 11. 2026 Patrick Harasser Bug Fixes, NetEye

Bug Fixes for NetEye 4.50

Update: Elastic Stack v9.5.6 also includes important security fixes. You can find more details here. Update of Elastic Stack to Version 9.5.6 Elastic Stack 9.5.6 is a maintenance release that brings a large set of stability, correctness and hardening fixes across Elasticsearch, Kibana, Fleet Server, Logstash, Elastic Agent, Beats, Elastic Observability, and Elastic Security. Elasticsearch…

Read More
29. 10. 2026 Patrick Harasser Bug Fixes, NetEye

NetEye 4.50 – Security Advisory (Icinga 2)

Disclaimer: The security issues referenced below do not yet have publicly disclosed CVE identifiers, so they are referenced by GHSA ID. This post will be updated as soon as CVEs become available. Important: Icinga 2 security update Type/Severity NetEye Product Security has rated this update as having a Medium security impact. Topic An update for the icinga…

Read More
29. 10. 2026 Patrick Harasser Bug Fixes, NetEye

NetEye 4 – Security Advisory (GLPI)

Disclaimer: The security issues below do not yet have publicly disclosed CVE identifiers, so details regarding their severity, impact, and potential attack vectors are not fully available at this time. This post will be updated as soon as additional information becomes available. Important: GLPI security update Type/Severity NetEye Product Security has rated this update as…

Read More
28. 10. 2026 Patrick Harasser Bug Fixes, NetEye

NetEye 4 – Security Advisory (Grafana)

Disclaimer: The CVEs referenced below have not yet been publicly disclosed, so details regarding their severity, impact, and potential attack vectors are not available at this time. This post will be updated as soon as additional information becomes publicly available. Update: The CVEs referenced below have now been publicly disclosed, and additional details have been…

Read More

Archive